Corporate Governance
By enhancing transparency, accountability, and efficiency, strengthen the balance between management and shareholders, establish effective risk management and internal control mechanisms, to enhance long-term corporate value and promote sustainable operations.
Information Security
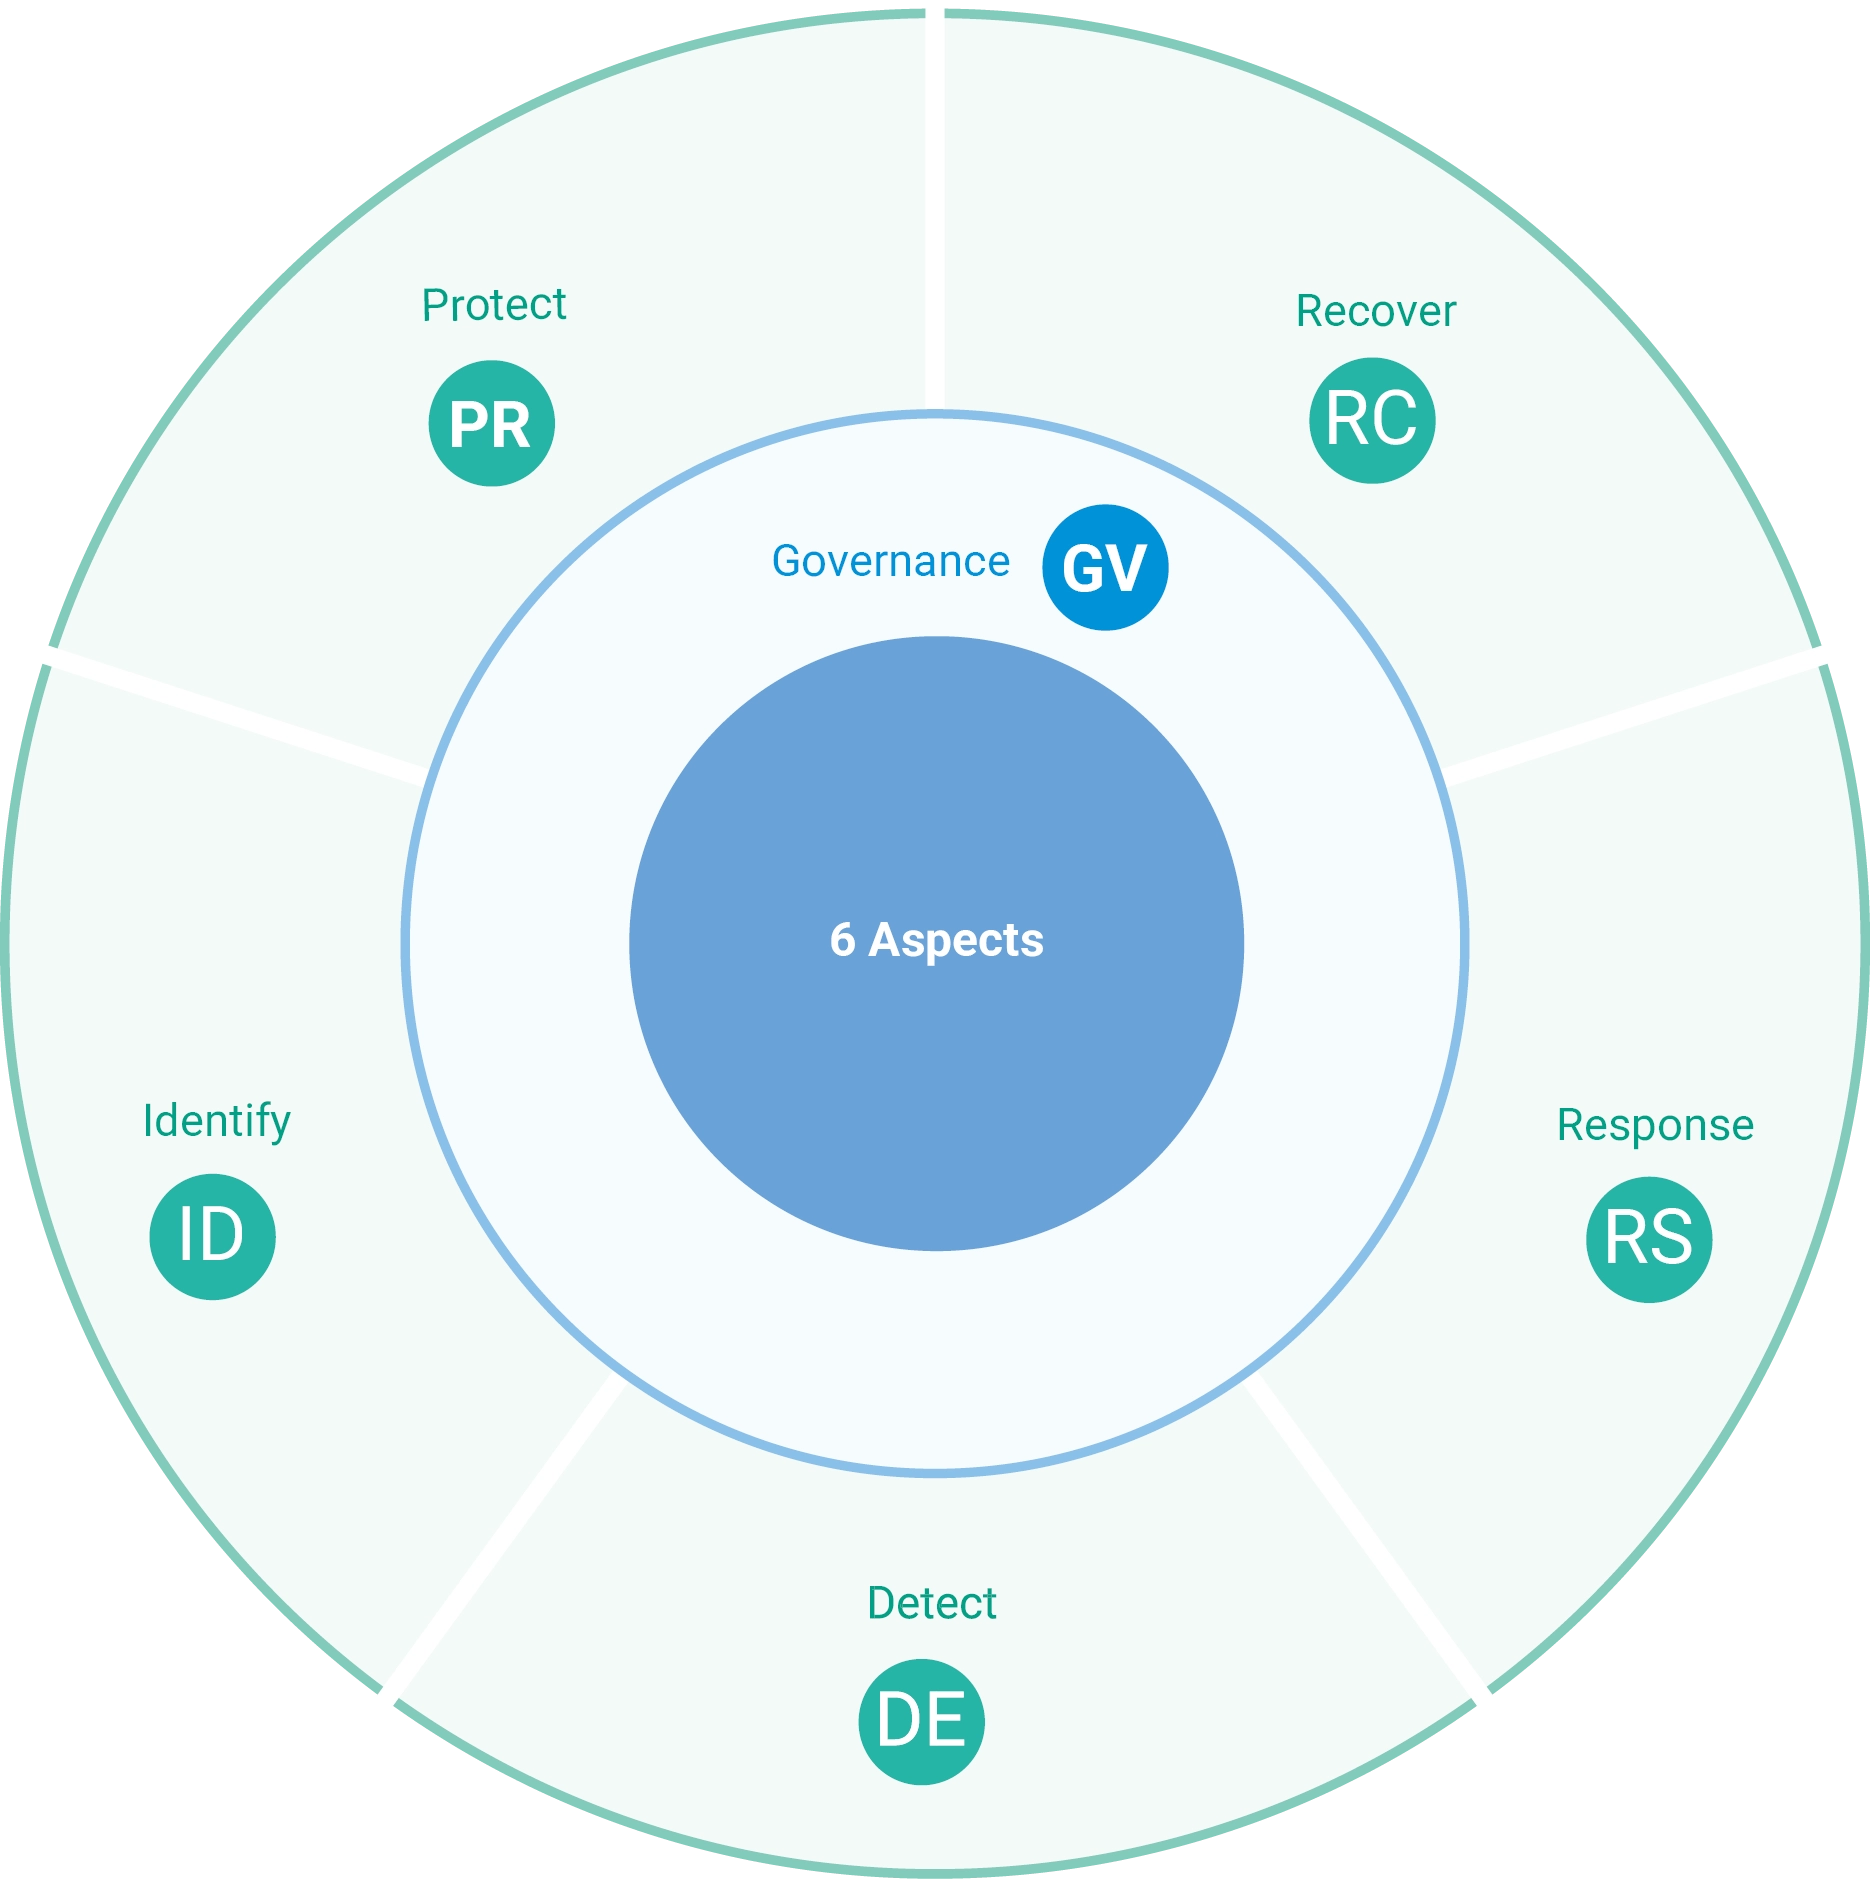
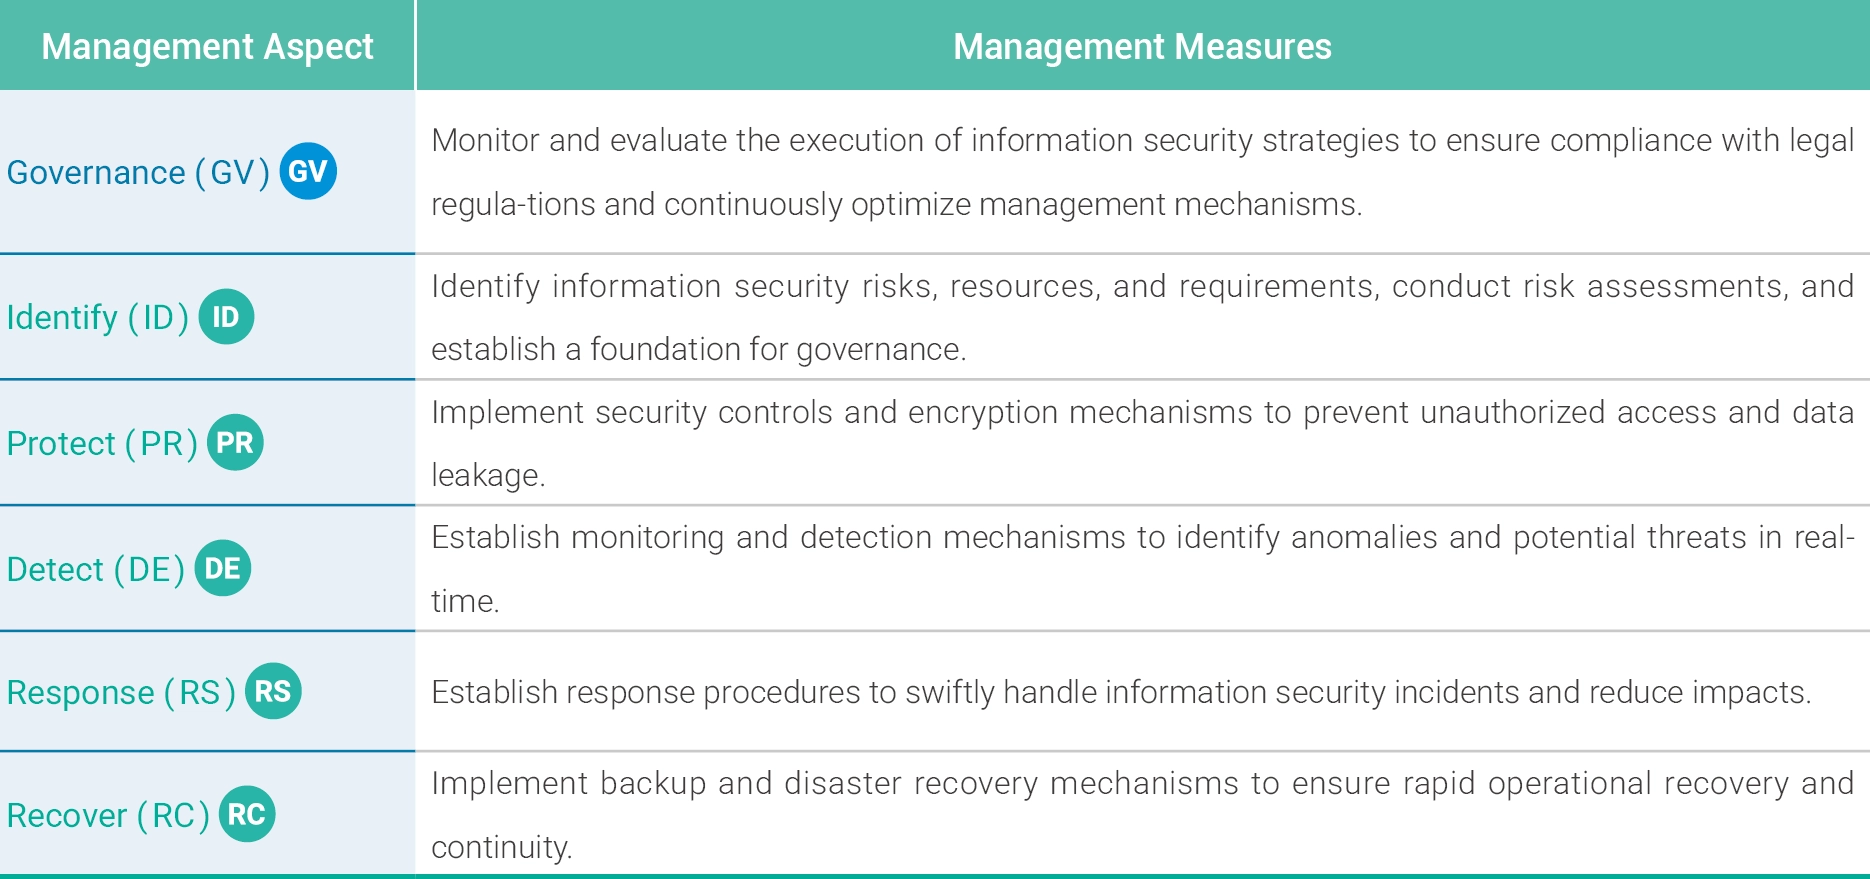
Phihong continuously enhances its information security management framework and strengthens protection capabilities through the Information Security Management Committee. The Committee promotes and implements a range of information security management measures to safeguard the Company’s intellectual property and customer data, raise employee awareness, and strengthen risk control mechanisms across the organization.
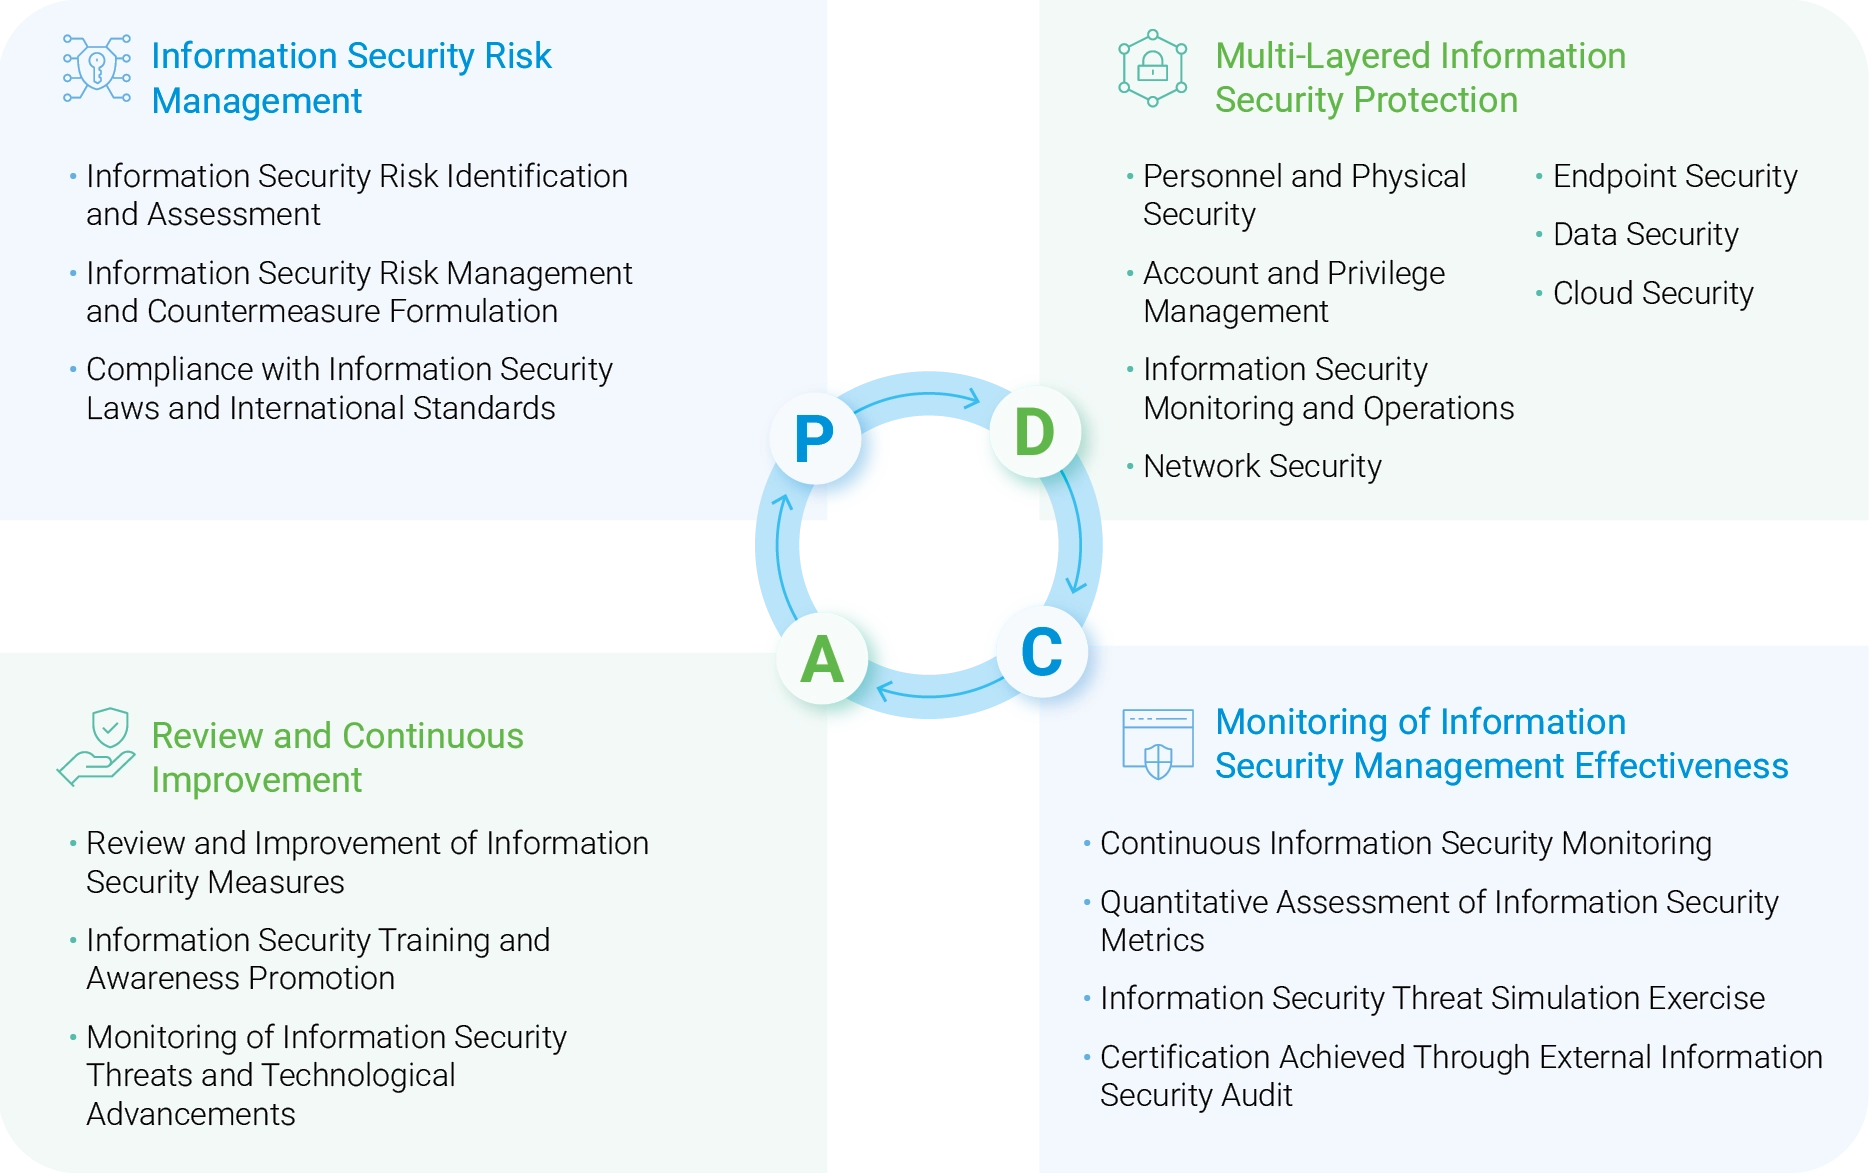
Phihong has elevated Information Security to the core of Corporate Governance by implementing the ISO 27001:2022 Information Security Management System (ISMS). Through the PDCA cycle, Phihong continuously improves and integrates information security management comprehensively into its operation and risk governance mechanism. Through a three-pronged approach of systems, technology, and culture, we enhance the confidentiality, integrity, and availability of IT assets. The Board of Directors regularly oversees these efforts to raise the overall governance pillar and decisionmaking quality, thereby establishing a resilient information security protection system.
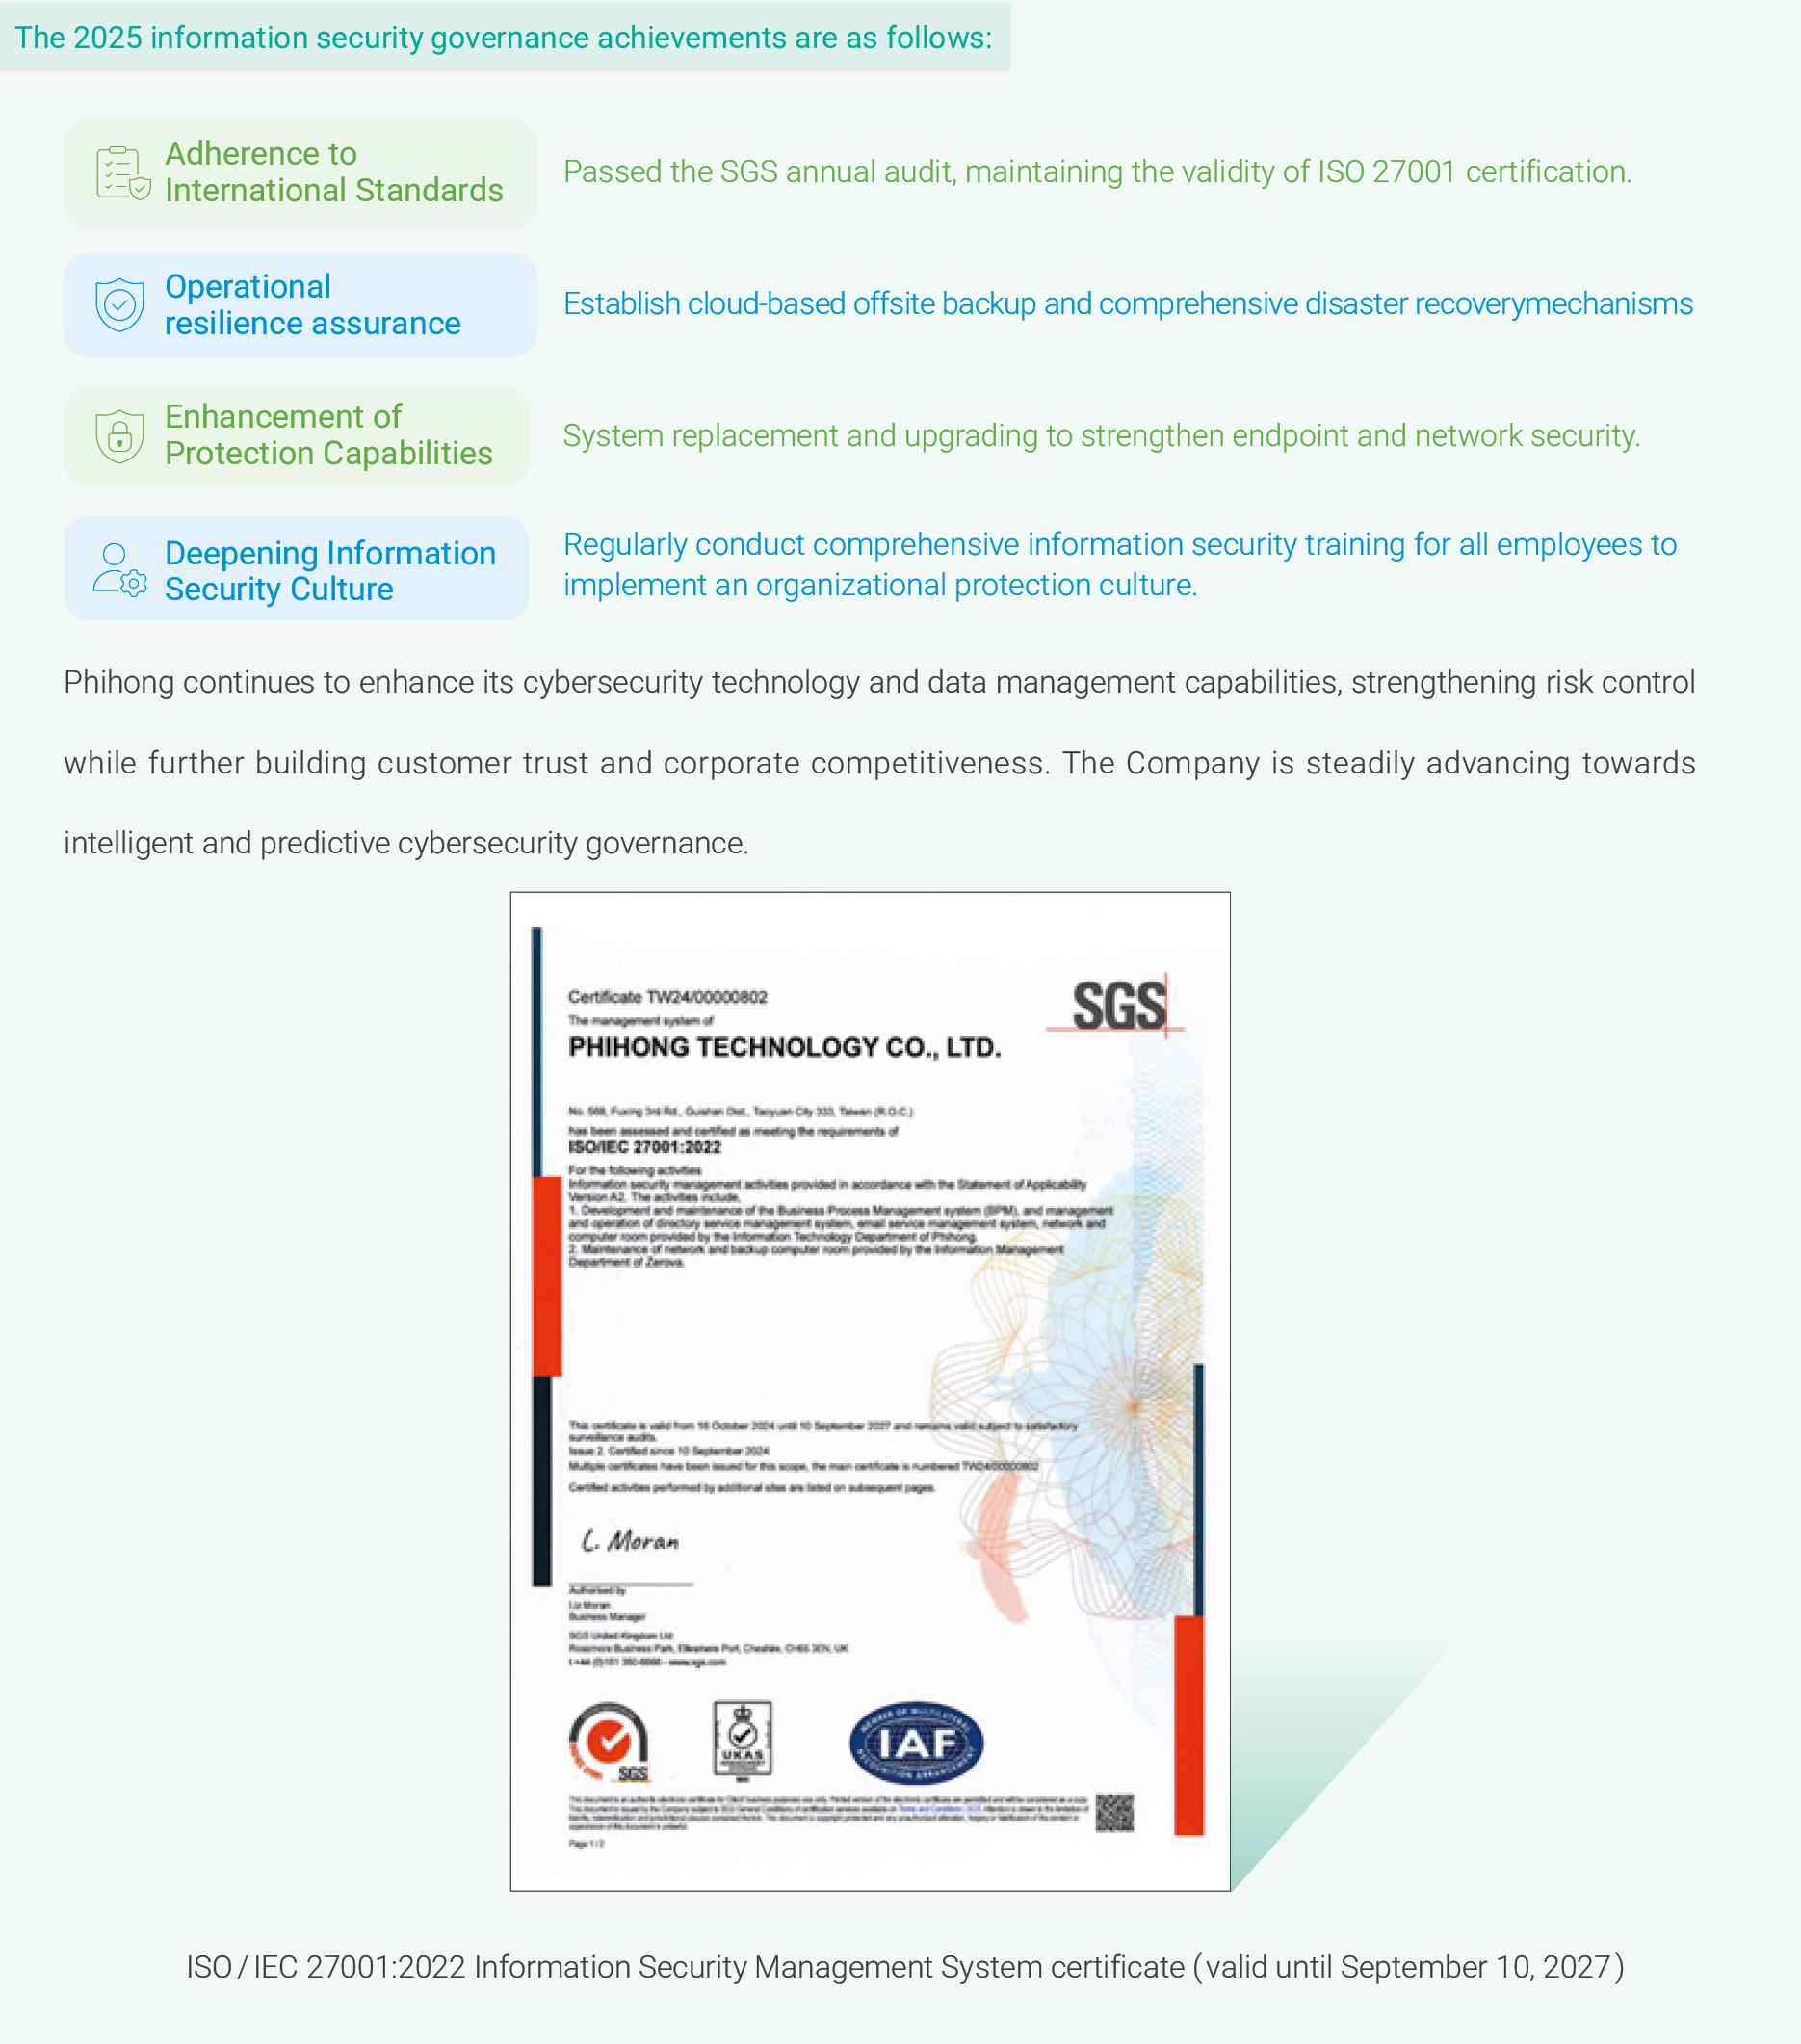
Phihong has incorporated Information Security into the core of Corporate Governance by establishing an internationally aligned information security management system. This ensures the confidentiality, integrity, and availability of information assets and effectively prevents unauthorized access and data leakage risks, safeguarding customer and business operation safety. The Company established the Information Security Committee in 2021, with the General Manager serving as the Chief Information Security Officer to oversee governance. In 2023, the Information Security Department was set up to strengthen policy formulation, risk management, and project implementation. Through institutionalized management reviews and risk assessment mechanisms, the department regularly reports cybersecurity performance to the Board of Directors, achieving governance pillar oversight.
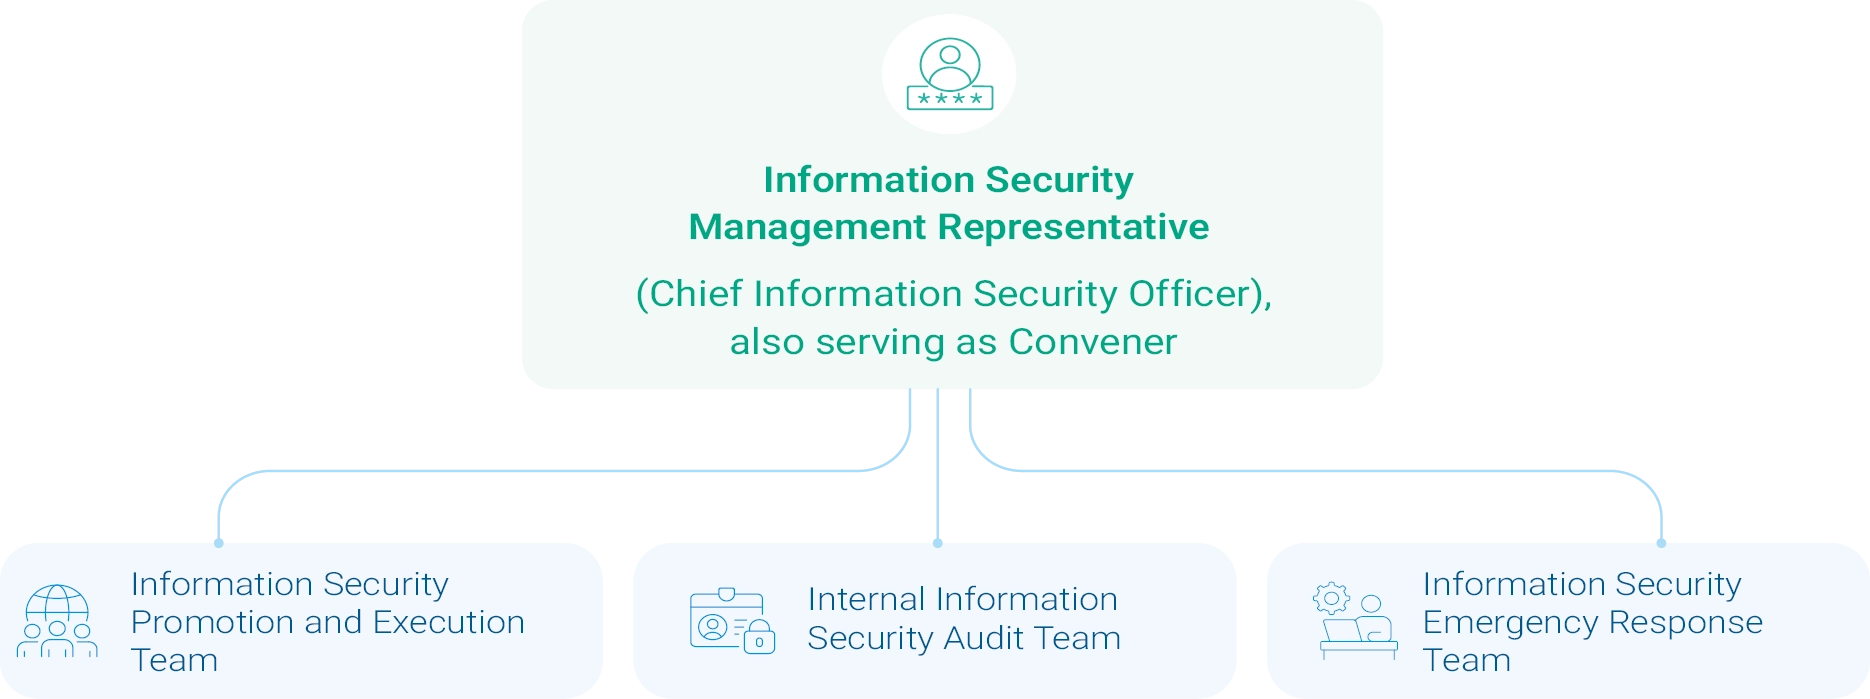
At the same time,Phihong’s cybersecurity governance framework covers dedicated units for management, audit, implementation, and response, forming a comprehensive protection system that continuously enhances corporate digital resilience. This reinforces stakeholder trust and demonstrates an international-level standard of cybersecurity governance.
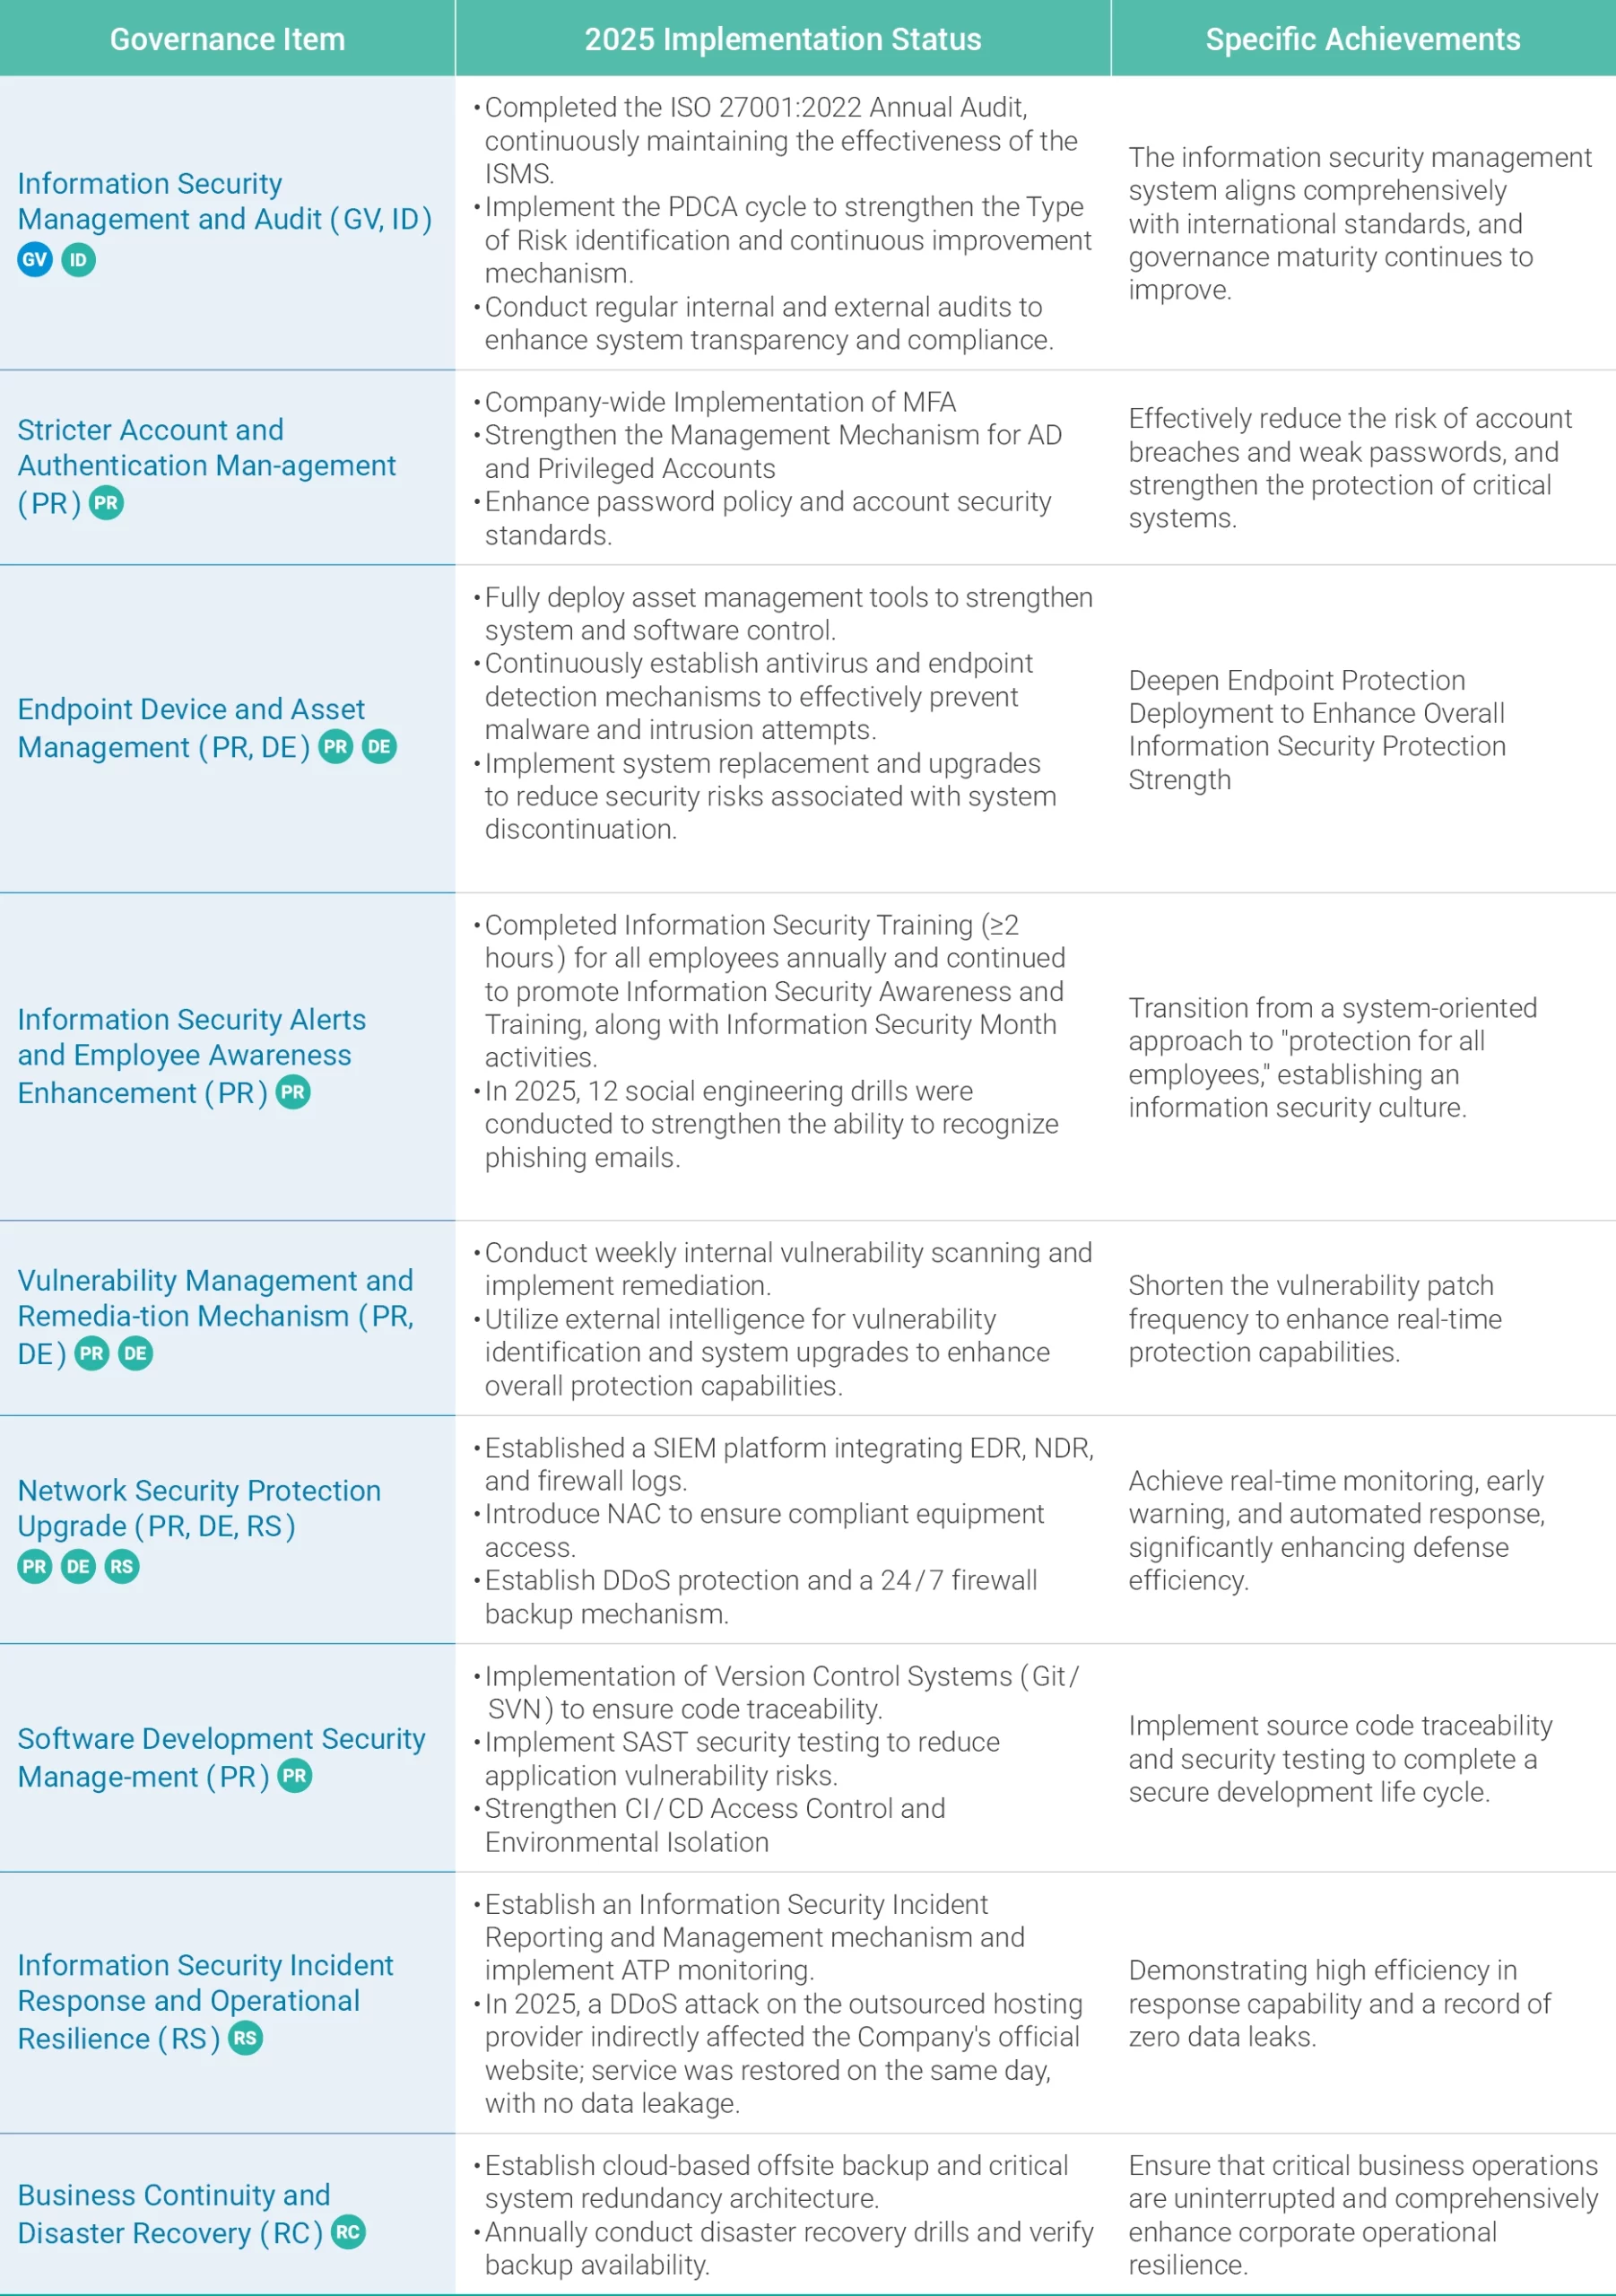
Phihong, using ISO 27001:2022 as the core framework, has established a comprehensive Information Security Governance system. By integrating risk-oriented management and digital monitoring mechanisms, Phihong has significantly enhanced its information security protection capabilities and operational resilience. In 2025, the Company will continue to improve the three major aspects of management systems, technical protection, and personnel awareness to ensure stable business operations and stakeholder trust.